Search result · source text not verified
[tests_count] automated, hourly tests, powered by a market-leading ecosystem of [integrations_count] integrations, give you continuous visibility into your compliance posture, collect audit evidence, and allow for easy collaboration with your stakeholders. Vanta automatically tracks if your personnel have completed required training, policy review, and actions—keeping them compliant and sending reminders when needed.
Products
Compliance Get compliant quickly and painlessly with automation.Get compliant without the chaos—Vanta automatically gathers the evidence you’ll need to get compliant, and continuously monitors your systems to make sure you stay compliant and secure.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
[tests_count] automated, hourly tests, powered by a market-leading ecosystem of [integrations_count] integrations, give you continuous visibility into your compliance posture, collect audit evidence, and allow for easy collaboration with your stakeholders. Plus, you can remediate issues faster with AI-generated code snippets, personalized to your infrastructure. Source ↗
Policy management
Source ↗Simplify policy creation and management with templates for every framework, a step-by-step policy builder to guide customization, and automated employee acceptance tracking.
Personnel management
Source ↗Ensure employees remain compliant with out-of-the-box security awareness training videos, in-app background checks, and customizable onboarding and offboarding workflows.
Pre-built and custom controls
Source ↗Use our out-of-the-box controls or bring your own, and Vanta AI will map your custom controls to Vanta ' s library of automated tests, getting to continuous monitoring even faster.
Vanta partner network
Source ↗Leverage Vanta’s extensive network of trusted auditors and partners to get the support you need. This includes vCISO services, managed service providers, complimentary penetration testing services, and more.
End-to-end audit support
Source ↗Plan, prep for, and execute your audits, all within Vanta. Manage issues to track and resolve audit findings, and easily communicate with your auditor to stay ultra-efficient through the audit process.
[integrations_count] integrations
Source ↗Vanta integrates deeply with tools ranging from cloud providers to task trackers to vulnerability scanners—and powers workflows like two-way task tracking, user access reviews, vulnerability SLA management, and more.
Personnel and Access Easily control user access and permissions.Vanta centralizes your critical processes—onboarding, offboarding, policy approvals, and awareness training.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Vanta automatically tracks if your personnel have completed required training, policy review, and actions—keeping them compliant and sending reminders when needed. Organize your personnel into Groups to assign relevant tasks and training. Build Groups in Vanta or import from your IdP. Source ↗
Personnel import
Source ↗Keep accurate personnel records by integrating directly with your IdP and HRIS software.
Personnel tasks
Source ↗Use built-in task templates and custom workflows to make sure your personnel tasks—including onboarding, recurring, and offboarding—are completed within your company’s SLAs.
Background checks
Source ↗Run discounted background checks directly from Vanta via Certn—a leading provider of background checks—or integrate with your current provider.
Security training
Source ↗Take advantage of in-platform security and privacy training videos, provided by Vanta, or integrate your own training providers.
Policy acceptance
Source ↗Centralize policy acceptance tracking for your audit by providing your employees with a simplified process to review and accept policies.
Groups
Source ↗Organize your personnel into Groups to assign relevant tasks and training. Build Groups in Vanta or import from your IdP.
Personnel reporting
Source ↗Understand your personnel compliance with a unified dashboard.
Access requests
Source ↗Request access to company systems directly from Vanta or Slack, and Vanta will route requests to system owners for approval and provisioning.
Access removal
Source ↗Monitor that system access is removed as a part of the offboarding process.
MFA tests
Source ↗Ensure MFA is enabled across your critical systems with Vanta ' s automated tests.
Ownership tests
Source ↗Detect newly created accounts in your systems and flag them when they ' re not connected to personnel in your organization.
MDM integration
Source ↗Integrate with your MDM to perform security checks on your company ' s devices, centralizing your audit evidence in Vanta.
Vanta Device Monitor
Source ↗Make sure your devices are secure with Vanta Device Monitor, our integrated compliance solution.
Device compliance tracking
Source ↗Enforce your security policies and programs, including password managers, hard drive encryption, screenlock, and antivirus software.
Risk Management Proactively manage risk to drive smarter decisions.Automate workflow and centralize your risk tracking to get results, faster.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Vanta automates reminders and workflows to regularly assess, review, and approve risks, freeing you up to focus on strategic risk analysis and proactive mitigation. Integrations with task-tracker systems like Jira, GitHub, and Asana allow you to assign action items in Vanta, while meeting teams where they’re already working. Source ↗
Risk register
Source ↗Track all of your risks in a single place—assign an owner, score inherent risk, set a treatment plan, and score residual risk.
Continuous risk monitoring
Source ↗Gain continuous insight into the controls and tests associated with a risk, with immediate notification when a tests fails.
Risk snapshots
Source ↗Take a moment-in-time snapshot of your risk register to be shared with auditors or downloaded.
Risk reporting
Source ↗Get up to speed fast with your risk report. View your risk heatmap, top risk categories, and risk trends over time, and easily share program status with stakeholders.
Risk mitigation planning
Source ↗Manage tasks and implement controls to reduce your risks.
Vendor risk
Source ↗Tie your overall risk management program to vendor risk management by linking findings added during a vendor security review to risk scenarios.
Third Party Risk Management Manage vendor onboarding and security reviews in one place.Vanta automatically pulls findings from your vendors SOC2 reports, DPAs, and questionnaires so your team focuses on high-stakes decisions, not paperwork.
Questionnaire Automation Automate security questionnaire responses.Vanta combs through your knowledge base of security documentation and previous questionnaires to generate responses for new questionnaires. Where an exact match is found, Vanta pulls that response through.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Make sure nothing slips through the cracks by assigning owners and approvers for each stage of the review process, and alerting them when it’s their turn to review. Source ↗
Automated notifications
Source ↗Never miss a beat with automated notifications for comments or response assignments over email or Slack.
Approval workflows
Source ↗Make sure nothing slips through the cracks by assigning owners and approvers for each stage of the review process, and alerting them when it’s their turn to review.
Knowledge base tagging
Source ↗Organize your knowledge base with custom tags to support multiple products, regions, and more, and generate tailored responses to questionnaires.
Synced policies
Source ↗Your knowledge base pulls in the latest Vanta policy documentation to ensure responses are always up-to-date and accurate.
Reporting
Source ↗Get insights into key metrics and trends to more effectively manage workload, measure business impact, and report ROI to leadership.
Multi-language responses
Source ↗Expand your reach and support global customers with automated questionnaires in Spanish, French, German, and Portuguese.
Trust CenterShowcase your compliance status and documentation.
Streamlined audits Automate audit prep and evidence collection.Vanta automates evidence collection, helps you collaborate with auditors, and gets you audit-ready—all with less hassle.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
With [tests_count] automated tests across [frameworks_count] frameworks, Vanta continuously monitors your controls and collects evidence in real time. So when it’s time to start your audit, everything’s already in place—making audits faster, easier, and smoother. Track evidence requests, submissions, and approvals in real time—and reuse evidence across audits—to save time and stay organized. Source ↗
Completeness and accuracy
Source ↗Only Vanta provides auditors access to test source data so auditors can verify automated testing—no screenshots required.
You decide what auditors see
Source ↗Choose which data to share with your auditor to maintain precision, protect privacy, and stay in control of your audit scope.
Evidence status tracking
Source ↗Track evidence requests, submissions, and approvals in real time—and reuse evidence across audits—to save time and stay organized.
Early audit access
Source ↗Give auditors early access to engagements or readiness checks, streamlining the audit process.
Issue management
Source ↗Log, track, and resolve issues as a centralized piece of your broader GRC program.
Seamless audit experience
Source ↗Work with Vanta and a trusted auditor through one coordinated process—fewer steps, faster audits, and everything managed in one platform.
Customer Commitments Centralize, track and act on every customer commitment.Scan and isolate contract obligations in seconds. The Commitments Agent bypasses dense legalese to identify high-stakes SLAs and custom security terms, turning 40-page PDFs into an actionable, real-time inventory of what you owe your customers.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Continuously sync with Ironclad, Salesforce, and Google Drive to keep every obligation current and mapped to the right Vanta controls. With 24/7 monitoring and proactive alerts, teams can address issues early, before a missed SLA turns into a renewal risk. Source ↗
AI Governance Govern AI as fast as you adopt it.With Vanta, you get a unified view of all your AI tools, agents, models, and MCPs. The Trust Graph connects each one to its owners, use cases, and accessible data and systems—so you always have the context to understand risk.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Meet AI frameworks and regulations with ease. Vanta connects your AI governance and compliance programs, continuously collecting proof and an audit trail of your AI governance practices—so you’re always ready to show compliance. Source ↗
Vanta AI Automate compliance and uncover insights with AI.The Vanta AI Agent is the sharpest GRC engineer you’ve never had to hire—working tirelessly across the Vanta platform to draft policies, complete questionnaires, and flag issues before they escalate. It’s not just automation; it’s an expert who’s got your back 24/7.
Source ↗ 2 ↗ 3 ↗ 4 ↗ 5 ↗ 6 ↗ 7 ↗ 8 ↗ 9 ↗ 10 ↗ 11 ↗ 12 ↗ 13 ↗ 14 ↗ 15 ↗ 16 ↗ 17 ↗ 18 ↗ 19 ↗Product page ↗
Combine the power of Vanta’s security and compliance knowledge with the world's best AI tools like Anthropic’s Claude, VS Code, Windsurf, and Cursor to help teams automate checks, catch issues earlier, and iterate with confidence—without slowing down development. Source ↗
Vanta APIBuild custom integrations and workflows.
SOC 2Get ready for a SOC 2 audit in weeks instead of months with Vanta’s automated compliance software.
ISO 27001Vanta makes it easy to craft policies, manage risks, and collect evidence you need to get ISO 27001 audit-ready—fast, automated, and built for trust.
GDPRSimplify GDPR compliance with Vanta. Centralize controls, evidence, and privacy workflows with Vanta—and reduce manual work with 400+ integrations and monitoring.
HIPAAVanta automates evidence collection with 400+ integrations, maps requirements to clear controls, and monitors compliance continuously.
HITRUSTVanta offers a pre-built HITRUST CSF solution, including e1, i1, and r2 to help you demonstrate trustworthy cybersecurity and health information protection.
NIST AI Risk Management FrameworkDemonstrate your commitment to mitigating AI risk with NIST AI RMF. From centralizing your AI risk policy to implementing governance, Vanta simplifies the end-to-end compliance process.
ISO 42001Communicate your dedication to responsible AI management with ISO 42001. ISO 42001 is an Artificial Intelligence Management System (AIMS) that helps organizations responsibly develop and use AI — emphasizing ethical considerations, transparency, and the necessity of continuous improvement.
FedRAMPVanta helps you prepare for FedRAMP authorization faster with guided documentation, policy templates, and centralized control tracking—built for SaaS and cloud providers selling to the U.S. federal government.
No matching products or features.
Customer feedback
@Bfaviero @TrustVanta I can’t believe I renewed my subscription a month ago with delve. Rip me, $14k down the drain lol. The advice was always a lil iffy. We paid $20k for a real pentest when they recommended going to a website that did a crap report for $20 lol
Search result · source text not verified
I'm an independent contractor and the company I contract ...
Vanta apparently automated security procedures for co pliance needs. It would give them control on how and when to secure your equipment.
Search result · source text not verified
Has anyone used Vanta for a pentest as part of SOC 2?
https://www.vanta.com/resources/accelerate-compliance-for-startups ... It would be interesting to see what someone at Vanta has to say. That ...
Search result · source text not verified
Automate and scale compliance
Put your audit prep on autopilot—and finish in 50% less time than doing it the traditional way with Vanta's automated compliance software.
Search result · source text not verified
Plans and Pricing
Thousands of customers depend on Vanta to streamline their SOC 2, ISO 27001, HIPAA, PCI, and GDPR. Get compliant quickly and painlessly with automation.
Search result · source text not verified
Blog
Get compliant quickly and painlessly with automation. Easily control user access and permissions. learn best practices, and get insight from experts on the ...
Search result · source text not verified
Read Customer Service Reviews of vanta.com
Contact info. United States. vanta.com. 3.1. Average. TrustScore 3 out of 5. 33 ... See how their reviews and ratings are sourced, scored, and moderated.
Search result · source text not verified
Read Customer Service Reviews of vanta.com | 2 of 2
vanta.com. 3.1. Average. TrustScore 3 out of 5. 33 reviews. 5-star. 4-star. 3-star ... See how their reviews and ratings are sourced, scored, and moderated.
No feedback found.
Marketing & Ads
GoogleVanta Incorporated
Original ad ↗ First shown Sep 4, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Jul 29, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Jul 29, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Sep 3, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026
MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaInactive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaInactive
Original ad ↗
Every AI Governance Program Starts Somewhere
See which step you’re on, and what comes next.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
You Know Compliance. What About Your AI?
A different kind of governance, a different kind of gap. Find out where yours sits.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
You Know Compliance. What About Your AI?
A different kind of governance, a different kind of gap. Find out where yours sits.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaActive
Original ad ↗
You Know Compliance. What About Your AI?
A different kind of governance, a different kind of gap. Find out where yours sits.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026MetaVantaInactive
Original ad ↗
You Know Compliance. What About Your AI?
A different kind of governance, a different kind of gap. Find out where yours sits.
Download
First shown Nov 11, 2026 · Last shown Nov 11, 2026GoogleVanta Incorporated
Original ad ↗ First shown Oct 13, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗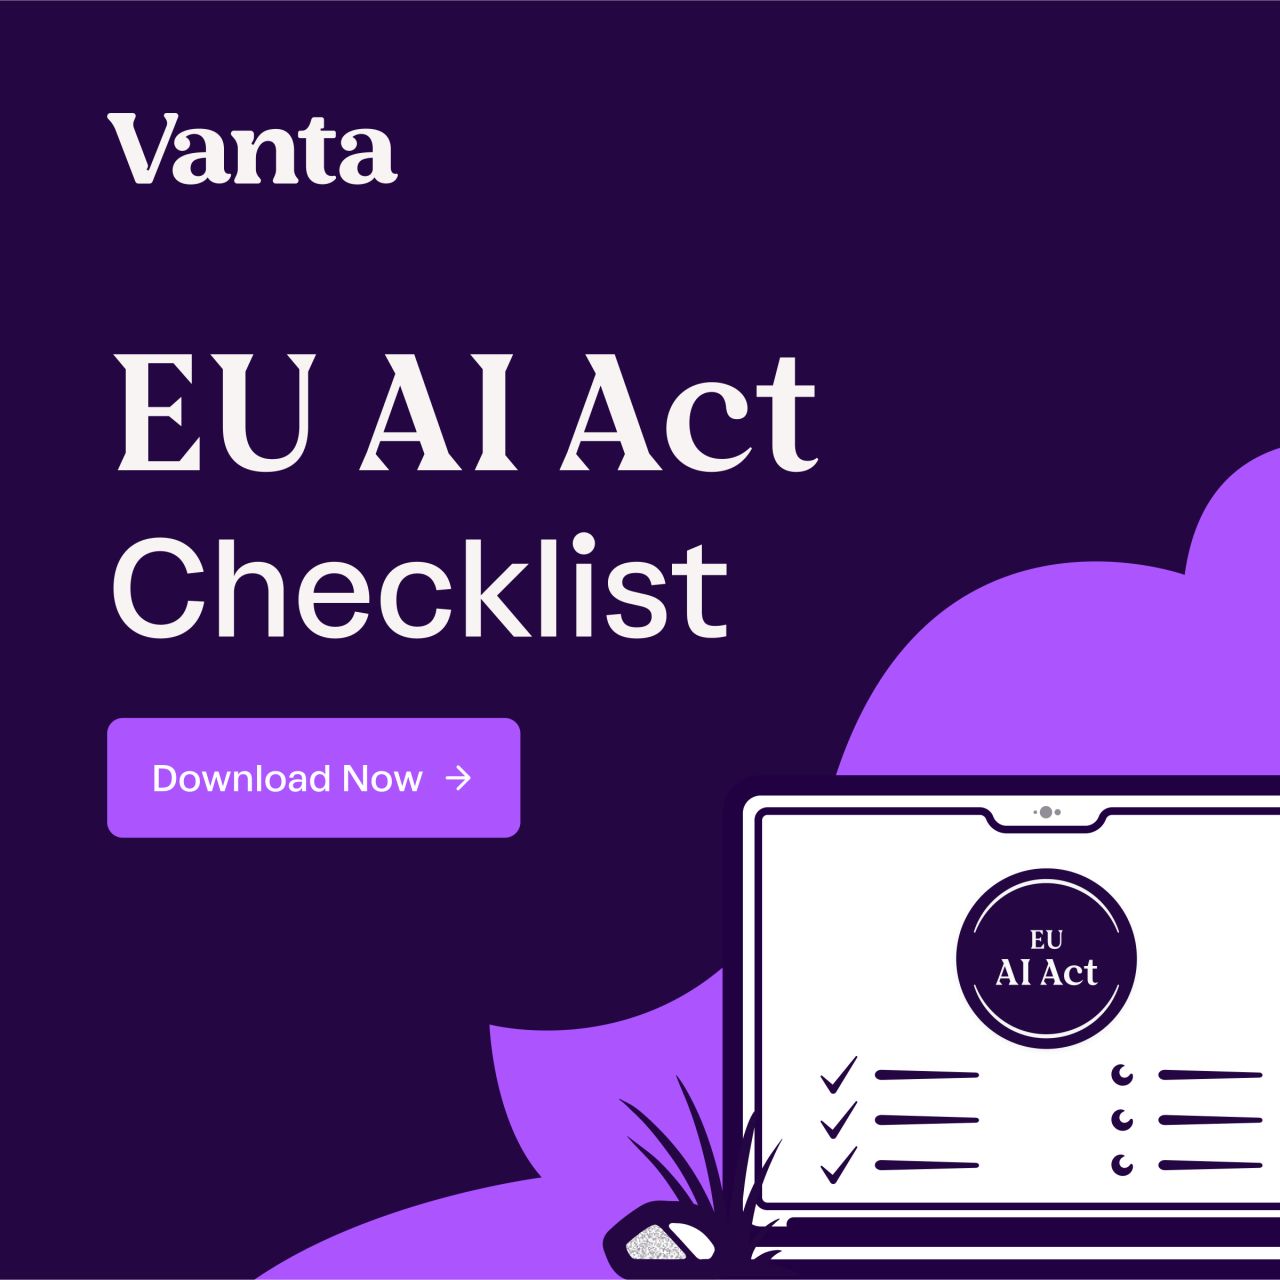
Show customers—and regulators—you take AI seriously
The EU AI Act is reshaping how companies build, deploy, and document AI. Use this checklist to see where you stand today, and what steps to take next. Whether you’re building in-house models or integrating third-party tools, staying ahead of AI compliance matters now more than ever.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Oct 13, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Oct 13, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗
See why teams are switching to Vanta
Vanta tests your controls every hour, so drift doesn't sit unnoticed until tomorrow. See the difference in a demo.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗
See why teams are switching to Vanta
200+ companies have already moved to Vanta. Book a demo and see what the switch looks like for your team.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗
See why teams are switching to Vanta
Your SOC 2 evidence shouldn't cost sprint time. Vanta pulls it automatically from 400+ integrations, no screenshots required.
Learn more
First shown Nov 4, 2026 · Last shown Nov 11, 2026
LinkedInVanta
Original ad ↗
Seven stalled deals, unblocked
A team of two, used Vanta to unblock seven stalled deals. Book a demo and see how.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗
Give your engineers the roadmap back
Every hour spent collecting evidence is an hour off the roadmap. Vanta automates it for SOC 2 and 35+ frameworks.
Learn more
First shown Nov 4, 2026 · Last shown Nov 11, 2026GoogleVanta Incorporated
Original ad ↗ First shown Nov 21, 2022 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗ First shown Sep 6, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInVanta
Original ad ↗Seven stalled deals, unblocked
A team of two, used Vanta to unblock seven stalled deals. Book a demo and see how.
Learn more
First shown Nov 4, 2026 · Last shown Nov 11, 2026
GoogleVanta Incorporated
Original ad ↗Compliance, Security, & Trust - Trusted by 16000+ Customers
Automated compliance software with continuous controls monitoring. Get a demo today.
First shown Sep 3, 2026 · Last shown Nov 11, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleVanta Incorporated
Original ad ↗Trusted by 16000+ Customers - The #1 Agentic Trust Platform
Trusted by 16000+ customers, from startup to enterprise. 1400+ automated, hourly tests and 400+ integrations keep your controls monitored. AI-Powered.
First shown Sep 3, 2026 · Last shown Nov 11, 2026Landing page unavailable: the ad source did not supply a destination URL.
LinkedInFrancesca Gettings
Original ad ↗
Calling something agentic doesn’t mean it actually is. Allow me to explain the difference.
First shown Nov 4, 2026 · Last shown Nov 11, 2026Landing page unavailable: the ad source did not supply a destination URL.
Website marketing
Get a custom demo with Vanta ↗
Vanta's demos are tailored to fit your organization's security and compliance requirements. Learn more about Vanta's automated compliance platform with a custom demo.
Observed Nov 11, 2026
New pages
How to assess data processors for privacy compliance ↗
Vanta + Pillar: The System of Runtime Action for AI Governance ↗
PIA vs DPIA: Key differences, requirements & when you need each ↗
What is cookie consent and why is it important? ↗
Govern AI and close bigger deals. The startup edition. ↗
The top 5 Rippling alternatives ↗
Your toughest AI governance questions vs. our GRC experts ↗
How to choose the right privacy management platform: 5 questions to ask ↗
Data protection impact assessments (DPIA): Guide and best practices ↗
The EU Cyber Resilience Act puts product makers on a 24-hour clock ↗
What is a DSAR? Your 101 guide to data subject access requests ↗
Key compliance frameworks in Australia: Privacy Act, CPS 234 & more ↗
PHP2Shell: The Critical PHP Vulnerabilities and The Vendor Blast Radius ↗
"Zombie work": Why nearly half of security leaders' tasks never get done ↗
How to implement CPS 234: A 7-step compliance guide ↗
How to build a CPS 230-aligned TPRM program ↗
Controllers vs processors vs subprocessors: All you need to know ↗
GDPR-compliant data processing agreements (DPAs): The 8 essential clauses ↗
Record of Processing Activities (RoPA): How to build and maintain it ↗
How to handle privacy questions during enterprise security reviews ↗
What is privacy management? Core components and how to build a program ↗
What is MAS TRM? A guide to Singapore’s risk management guidelines ↗
How Essential Eight impacts government contracting in Australia ↗
Key compliance frameworks in Singapore: PDPA, MAS TRM, Cybersecurity Act, and more ↗
Inside the builder renaissance. Is your startup playing to win? ↗
Which cybersecurity and compliance frameworks apply to your business in Japan? ↗
Australia’s Children’s Online Privacy Code: Does it impact your business? ↗
Introducing the Vanta Control Framework: One lens for every framework ↗
Steal our blueprint. GRC engineering at Vanta and Synthesia. ↗
How the Essential Eight influences cyber insurance premiums in Australia ↗
5 best GRC software solutions for enterprise teams in 2026 ↗
What is NZISM? Guide to New Zealand's Information Security Manual ↗
How APRA’s AI guidance impacts banks and insurers in Australia ↗
What is ISMS-P and how it aligns with ISO 27001 and ISO 27701 ↗
SOCI and CIRMP: The cybersecurity frameworks Australian critical infrastructure operators can use ↗
AI anxiety is showing up on the org chart ↗
The cache miss that made our agent faster ↗
The best security questionnaire automation software for 2026 ↗
The best risk management software for enterprises ↗
Australian Privacy Principles: A compliance guide for small businesses ↗
The 5 best GRC software solutions for CMMC compliance in 2026 ↗
The best compliance management software for 2026 ↗
The best risk management software for 2026 ↗
Design tools around information, not APIs ↗
Zlatko Unger, CISO Expert at Wiz, and the helpful assistant | The Tabletop ↗
DIFC Regulation 10: AI system certification requirements orgs need to know ↗
You've adopted AI. Now what about governance? ↗
Build Compliance into your AI Stack with Vanta ↗
Zombie work is biting CISOs ↗
The 5 best compliance software solutions for enterprises in 2026 ↗
How to define your third-party risk criteria ↗
The 5 best options for compliance privacy software ↗
Fourth-party risk management: How to identify and manage downstream risk ↗
Continuous risk monitoring in third-party risk management is non-negotiable: Here’s why ↗
Vanta Delivers: Build without limits. ↗
Give your agents capabilities ↗
The guide to HIPAA regulations and rules for healthcare companies and their vendors ↗
AI vendors can change their risk profile between reviews, and most oversight programs never notice ↗
What are the best GRC software solutions of 2026? ↗
Will Bengtson, CISO at C1, and the respected engineer | The Tabletop ↗
Are zero-touch assessments the future of security reviews? ↗
C5:2026 readiness checklist ↗
Cybersecurity risk management: A complete guide for security teams ↗
How to evaluate and choose risk management software ↗
What is continuous security monitoring? ↗
NIST SP 800-161: A guide to C-SCRM practices ↗
Introducing the 2026 Vanta 25 to Trust Award winners ↗
Why enterprise leaders choose Vanta over Drata to prove and manage trust ↗
Supply chain risk management: What it is and why enterprises need it ↗
Govern AI as fast as you adopt it ↗
NIST AI Risk Management Framework (AI RMF): Everything you need to know ↗
You can build verifiers for messy problems ↗
Risk management maturity model: How to assess and improve your program ↗
Sean Cassidy, CISO at Plaid, and the moving mouse | The Tabletop ↗
Your complete guide to compliance management software ↗
How to build a continuous feedback loop between risk management and control monitoring ↗
Introducing AI Governance from Vanta ↗
Guide to measuring risk management performance with the right focus areas ↗
Meet Ilma, our mascot. (She prefers Compliance Connoisseur.) ↗
How to create risk reports for operations, executives, and auditors ↗
The AI governance confidence gap: Why trust in AI is running ahead of the capacity to govern it ↗
Enterprise risk designations and multiple risk registers: when are they relevant? ↗
Introducing your compliance co-founder ↗
Compliance meets AI: Designing products that are secure from the start with Vanta and AWS ↗
How to design a risk register: A guide for GRC practitioners ↗
Jason Chan, ex-Netflix, and the trusted contractor | The Tabletop ↗
The 5 best GDPR compliance software options for 2026 ↗
How to report risk to leadership and the board: A guide for security and GRC executives ↗
Run Compliance from Claude, Cursor, and Codex with Vanta ↗
What is cyber resilience? Why it matters and how to build it ↗
5 reasons why spreadsheets for risk management don’t work (and what you can do instead) ↗
AI in risk management: Practical applications and considerations ↗
The background agent that outgrew me ↗
The best SOC 2 compliance software for 2026 ↗
The best third party risk management software solutions for enterprises ↗
Giving the Vanta Agent a computer ↗
The best ISO 27001 compliance software for 2026 ↗
7 risk management best practices as regulatory pressure intensifies in 2026 ↗
The hallucinating bot with Alex Stamos, CPO at Corridor | The Tabletop ↗
What is a risk register? Best practices for keeping It actionable ↗
What is Enterprise Risk Management (ERM)? Everything you need to know ↗
Modified Source ↗
the tools you need to grow your vanta partnership ↗
Modified Source ↗
governing ai at the speed you ship it ↗
Modified Source ↗
law firms ↗
Modified Source ↗
partner program ↗
Modified Source ↗
ai governance ↗
Modified Source ↗
fin ↗
Modified Source ↗
metluma ↗
Modified Source ↗
gdpr compliance for us companies ↗
Modified Source ↗
ai governance maturity assessment ↗
Modified Source ↗
vantacon ↗
Modified Source ↗
eight sleep ↗
Modified Source ↗
Cut risk assessment time by 50% ↗
Modified Source ↗
faq ↗
Modified Source ↗
The fast, trusted way to earn your SOC 2 ↗
Modified Source ↗
Build on trust ↗
Modified Source ↗
reed smith ↗
Modified Source ↗
netskope ↗
Fast, accurate audits, from readiness to report ↗
Modified Source ↗
rippling ↗
Modified Source ↗
its not you its your platform three teams on leaving drata for vanta ↗
Modified Source ↗
vanta x evotek 49ers game experience ↗
Modified Source ↗
8 steps to make your website gdpr compliant ↗
Modified Source ↗
cybersecurity laws regulations uk ↗
Modified Source ↗
the gdpr basics your business needs to know ↗
Modified Source ↗
pricing ↗
Modified Source ↗
soc 2 ↗
Modified Source ↗
vanta delivers ↗
Modified Source ↗
calm pliance ↗
Modified Source ↗
rsa ↗
Modified Source ↗
Build a bulletproof AWS FTR submission ↗
Modified Source ↗
integrations ↗
Modified Source ↗
about ↗
Modified Source ↗
specbook ai ↗
Modified Source ↗
vanta led executive dinner nyc ↗
Modified Source ↗
veriproof ↗
Modified Source ↗
ai governance ↗
Modified Source ↗
eu ai act guide ↗
Modified Source ↗
gdpr compliance for saas ↗
Modified Source ↗
govern ai and close bigger deals the startup edition ↗
Modified Source ↗
govern ai and close bigger deals the startup edition apj ↗
Modified Source ↗
your toughest ai governance questions vs our grc experts ↗
Modified Source ↗
training ↗
Modified Source ↗
agenda ↗
Modified Source ↗
CMMC compliance, simplified ↗
Modified Source ↗
Prove your AI agents are truly safe ↗
Modified Source ↗
Speed up security reviews with AI-powered Questionnaire Automation ↗
Modified Source ↗
Built-in assurance for every customer commitment ↗
Modified Source ↗
Remediate risk up to 45% faster 1 ↗
Built in. Always on. One step ahead. ↗
Modified Source ↗
trust tour ↗
Modified Source ↗
Manage personnel compliance from one place, efficiently ↗
Modified Source ↗
tprm ↗
Modified Source ↗
forrester wave grc ↗
Modified Source ↗
idc marketscape ↗
Modified Source ↗
data subject rights gdpr ↗
Modified Source ↗
what is gdpr ↗
Modified Source ↗
Answer the AI question once, not every deal ↗
Modified Source ↗
iso 42001 ↗
Modified Source ↗
Prove trust to customers before they ask with Trust Center ↗
Modified Source ↗
find a partner ↗
Modified Source ↗
vanta api ↗
Modified Source ↗
Grow globally with ISO 27001 compliance ↗
Modified Source ↗
A new way to GRC ↗
Modified Source ↗
careers ↗
Modified Source ↗
demo de ↗
Modified Source ↗
home ↗
Modified Source ↗
healthcare ↗
Modified Source ↗
steal our blueprint grc engineering at vanta and synthesia ↗
Modified Source ↗
steal our blueprint grc engineering at vanta and synthesia ↗
Modified Source ↗
kindlee contextual ai fairness ↗
Modified Source ↗
soc 2 for startups ↗
Modified Source ↗
build at ai speed and stay in control with aws and vanta ↗
Modified Source ↗
build at ai speed and stay in control with aws and vanta ↗
Modified Source ↗
additional frameworks ↗
Modified Source ↗
support metrics ↗
Modified Source ↗
ally security ↗
Modified Source ↗
nist csf vs iso 27001 ↗
Modified Source ↗
swif ↗
Modified Source ↗
swif ↗
Modified Source ↗
gdpr and soc 2 ↗
Modified Source ↗
continuous control monitoring ↗
Modified Source ↗
companies that hired chief trust officers ↗
Modified Source ↗
inside the builder renaissance is your startup playing to win ↗
Modified Source ↗
inside the builder renaissance is your startup playing to win ↗
Modified Source ↗
badges ↗
Modified Source ↗
gdpr compliance audit ↗
Modified Source ↗
carter newell lawyers ↗
Modified Source ↗
dust ↗
Modified Source ↗
customer wins trust center ↗
Modified Source ↗
introducing the vanta trusted network apj ↗
Modified Source ↗
its not you its your platform three teams on leaving drata for vanta ↗
Modified Source ↗
customers ↗
Modified Source ↗
Spend 82% less time per framework and attestation related audit ↗
Modified Source ↗
securance ↗
Modified Source ↗
hipaa ↗
Modified Source ↗
eu bundle ↗
Modified Source ↗
stamprise ↗
Modified Source ↗
introducing the vanta trusted network ↗
Modified Source ↗
Demonstrate strong AI governance with ISO 42001 ↗
Modified Source ↗
hex networks ↗
Modified Source ↗
googledrive ↗
Modified Source ↗
upcover ↗
Modified Source ↗
fedramp 20x ↗
Modified Source ↗
fedramp marketplace ↗
Modified Source ↗
gdpr and ccpa ↗
Modified Source ↗
gdpr and usdp ↗
Modified Source ↗
gdpr compliance checklist guide ↗
Modified Source ↗
ai governance ↗
Modified Source ↗
business continuity plan ↗
Modified Source ↗
compliance management ↗
Modified Source ↗
compliance management system ↗
Modified Source ↗
compliance programs ↗
Modified Source ↗
compliance reporting ↗
Modified Source ↗
continuous compliance ↗
Modified Source ↗
cybersecurity governance ↗
Modified Source ↗
data governance ↗
Modified Source ↗
grc audit ↗
Modified Source ↗
grc benefits ↗
Modified Source ↗
incident response plan ↗
Modified Source ↗
internal compliance audit ↗
Modified Source ↗
it governance ↗
Modified Source ↗
preparing for a compliance audit ↗
Modified Source ↗
risk assessment matrix ↗
Modified Source ↗
risk assessment methodologies ↗
Modified Source ↗
risk management ↗
Modified Source ↗
risk management automation ↗
Modified Source ↗
risk management frameworks ↗
Modified Source ↗
risk management strategy ↗
Modified Source ↗
security compliance ↗
Modified Source ↗
the role of ccm automation and ai in grc ↗
Modified Source ↗
user access reviews ↗
Modified Source ↗
automated iso 27001 vs manual iso 27001 ↗
Modified Source ↗
benefits of compliance automation iso 27001 ↗
Modified Source ↗
benefits of iso 27001 certification ↗
Modified Source ↗
guide to iso 27701 ↗
Modified Source ↗
how gdpr and iso 27001 work together ↗
Modified Source ↗
how long does it take to get iso certified ↗
Modified Source ↗
iso 27001 compliance checklist ↗
Modified Source ↗
iso 27001 vs iso 27701 ↗
Modified Source ↗
iso 27001 vs soc 2 what is the difference ↗
Modified Source ↗
mapping common criteria soc 2 and iso 27001 ↗
Modified Source ↗
automation for auditors and organizations ↗
Modified Source ↗
iso 27001 vs soc 2 ↗
Modified Source ↗
soc 2 badge ↗
Modified Source ↗
ssae 16 vs ssae18 ↗
Modified Source ↗
what is soc 1 ↗
Modified Source ↗
third party risk requirements gdpr ↗
Modified Source ↗
third party risk requirements hipaa ↗
Modified Source ↗
third party risk requirements iso 27001 ↗
Modified Source ↗
third party risk requirements pci dss ↗
Modified Source ↗
third party risk requirements soc 2 ↗
Modified Source ↗
vendor risk assessment questionnaire ↗
Modified Source ↗
vendor risk management framework ↗
Modified Source ↗
chief trust officer ↗
Modified Source ↗
customer trust ↗
Modified Source ↗
security questionnaires ↗
Modified Source ↗
security questionnaires explained ↗
Modified Source ↗
what is a trust center ↗
Modified Source ↗
what is a trust management platform ↗
Modified Source ↗
amtivo ↗
Modified Source ↗
eu ai act checklist ↗
Modified Source ↗
mid market ↗
Modified Source ↗
schneider downs ↗
Modified Source ↗
codat ↗
Modified Source ↗
noventiq ↗
Modified Source ↗
synthesia ↗
Modified Source ↗
best third party risk management software ↗
Modified Source ↗
fintech ↗
Modified Source ↗
trust management platform ↗
Modified Source ↗
vanta platform ↗
Modified Source ↗
c5 ↗
Modified Source ↗
attackerview ↗
Modified Source ↗
attackerview ↗
Modified Source ↗
linear ↗
Modified Source ↗
vercel ↗
Modified Source ↗
pci dss ↗
Modified Source ↗
demo ↗
Modified Source ↗
grsee consulting ↗
Modified Source ↗
brand mascot ↗
Modified Source ↗
how to choose a grc solution ↗
Modified Source ↗
claudes compliance api ↗
Modified Source ↗
accelerating growth compliance anz ↗
Modified Source ↗
accelerating growth compliance europe ↗
Modified Source ↗
categories of iso 27001 controls ↗
Modified Source ↗
compliance statistics ↗
Modified Source ↗
frameworks for success leveraging security privacy frameworks to scale a growing business ↗
Modified Source ↗
how gdpr and iso 27001 work together ↗
Modified Source ↗
how much does it cost to get iso 27001 certified ↗
Modified Source ↗
is all compliance regulatory compliance ↗
Modified Source ↗
iso 27001 for startups what every startup needs to know ↗
Modified Source ↗
iso 42001 ↗
Modified Source ↗
soc 2 and iso 27001 take advantage of common criteria mapping for compliance ↗
Modified Source ↗
soc 2 vs iso 27001 compliance why you need both ↗
Modified Source ↗
the ultimate guide iso 27017 ↗
Modified Source ↗
the ultimate guide to iso 27701 ↗
Modified Source ↗
vanta helps companies accelerate growth with 10 new security and data privacy compliance frameworks ↗
Modified Source ↗
enterprise ↗
Modified Source ↗
ai governance the framework the pitfalls the playbook ↗
Modified Source ↗
ai governance the framework the pitfalls the playbook ↗
Modified Source ↗
bitbucket ↗
Modified Source ↗
youve adopted ai now what about governance ↗
Modified Source ↗
youve adopted ai now what about governance ↗
Modified Source ↗
jumpcloud ↗
Modified Source ↗
continuous monitoring ↗
Modified Source ↗
build compliance into your ai stack with vanta ↗
Modified Source ↗
build compliance into your ai stack with vanta ↗
Modified Source ↗
vanta x shi at away venice compliance packed ↗
Modified Source ↗
the eu ai act roadmap ↗
Modified Source ↗
gdpr ↗
Modified Source ↗
how to choose hipaa compliance software ↗
Modified Source ↗
soc 2 compliance requirements ↗
Modified Source ↗
veremark ↗
Modified Source ↗
cyber risk institute profile ↗
Modified Source ↗
eu ai act ↗
Modified Source ↗
workspaces ↗
Modified Source ↗
Meet your compliance requirements—no matter the framework ↗
Modified Source ↗
access reviews ↗
Modified Source ↗
Safeguard sensitive data with HITRUST CSF ↗
Modified Source ↗
iso 9001 ↗
Modified Source ↗
ofdss ↗
Modified Source ↗
mvsp ↗
Modified Source ↗
cis v8 ↗
Modified Source ↗
sspa ↗
Modified Source ↗
iso 27017 ↗
Modified Source ↗
iso 27018 ↗
Modified Source ↗
sox itgc ↗
Modified Source ↗
iso 27701 ↗
Modified Source ↗
nist csf 2 ↗
Modified Source ↗
tisax ↗
Modified Source ↗
iso 22301 ↗
Modified Source ↗
nydfs nycrr ↗
Modified Source ↗
fedramp 20x ↗
Modified Source ↗
nist 800 171 ↗
Modified Source ↗
nist 800 53 ↗
Modified Source ↗
FedRAMP simplified for a faster path to Certification ↗
Modified Source ↗
cps 234 ↗
Modified Source ↗
essential eight ↗
Modified Source ↗
cyber essentials ↗
Modified Source ↗
dora ↗
Modified Source ↗
nis2 ↗
Modified Source ↗
cjis ↗
Modified Source ↗
Mitigate AI risk with the NIST AI Risk Management Framework ↗
Modified Source ↗
usdp ↗
Modified Source ↗
ccpa ↗
Modified Source ↗
The fastest path to GDPR compliance ↗
Modified Source ↗
Automate HIPAA compliance and keep protected health information secure ↗
Modified Source ↗
pendo ↗
Modified Source ↗
whats new ↗
Modified Source ↗
soc 1 vs soc 2 which one do you need ↗
Modified Source ↗
flaconi ↗
Modified Source ↗
vanta delivers build without limits ↗
Modified Source ↗
eu ai act ↗
Modified Source ↗
sydney ↗
Modified Source ↗
jira ↗
Modified Source ↗
cmmc ↗
Modified Source ↗
tuv nord ↗
Modified Source ↗
vanta delivers build without limits apac ↗
Modified Source ↗
vanta delivers build without limits ↗
Modified Source ↗
aws ↗
Modified Source ↗
skills ↗
Modified Source ↗
colors ↗
Modified Source ↗
typography ↗
Modified Source ↗
voice and tone ↗
Modified Source ↗
logo ↗
Modified Source ↗
introduction ↗
Modified Source ↗
compliance audit software ↗
Modified Source ↗
government ↗
Modified Source ↗
servicenow ↗
Modified Source ↗
archer ↗
Modified Source ↗
optro ↗
Modified Source ↗
onetrust ↗
Modified Source ↗
secureframe ↗
Modified Source ↗
sprinto ↗
Modified Source ↗
delve ↗
Modified Source ↗
drata ↗
Modified Source ↗
best hipaa compliance software ↗
Modified Source ↗
what is soc 2 ↗
Modified Source ↗
sevaka ↗
Modified Source ↗
the tabletop with zlatko unger ↗
Modified Source ↗
vanta delivers internal risk ↗
Modified Source ↗
uk ↗
Modified Source ↗
soc block ↗
Modified Source ↗
government apj ↗
Modified Source ↗
vanta for growth ↗
Modified Source ↗
trust maturity report ↗
Modified Source ↗
iso 27001 ↗
Modified Source ↗
gdpr ↗
Modified Source ↗
soc 2 ↗
Modified Source ↗
demo uk ↗
Modified Source ↗
vanta vs competitors v1 ↗
Modified Source ↗
service providers ↗
Modified Source ↗
enhanced security risk management ↗
Modified Source ↗
cmmc compliance automation ↗
Modified Source ↗
cmmc controls ↗
Modified Source ↗
soc 2 audit cost ↗
Modified Source ↗
soc 2 trust service criteria ↗
Modified Source ↗
soc 2 type 1 ↗
Modified Source ↗
soc 2 type 2 ↗
Modified Source ↗
best fedramp compliance software ↗
Modified Source ↗
best trust center software ↗
Modified Source ↗
what is hipaa compliance ↗
Modified Source ↗
hitrust compliance ↗
Modified Source ↗
guide to iso 27017 ↗
Modified Source ↗
what is an information security management system ↗
Modified Source ↗
what is iso 27001 certification ↗
Modified Source ↗
iso 42001 guide ↗
Modified Source ↗
granitestack ↗
Modified Source ↗
the tabletop with alex stamos ↗
Modified Source ↗
the tabletop with jason chan ↗
Modified Source ↗
the tabletop with will bengtson ↗
Modified Source ↗
the tabletop with sean cassidy ↗
Modified Source ↗
vantacon vip dinner ↗
Modified Source ↗
features ↗
Modified Source ↗
gdpr compliance benefits ↗
Modified Source ↗
cyber vendor risk management ↗
Modified Source ↗
third party risk management ↗
Modified Source ↗
vendor due diligence ↗
Modified Source ↗
vendor onboarding ↗
Modified Source ↗
vendor relationship management ↗
Modified Source ↗
vendor risk assessment report ↗
Modified Source ↗
vendor risk assessments ↗
Modified Source ↗
vendor risk management ↗
Modified Source ↗
vendor risk management metrics kpis ↗
Modified Source ↗
vendor risk management software ↗
Modified Source ↗
die iso 27001 compliance checkliste bestatigung ↗
Modified Source ↗
die soc 2 compliance checkliste bestatigung ↗
Modified Source ↗
the builder boom breaking security ↗
Modified Source ↗
when tokenmaxxing leads to riskmaxxing ↗
Modified Source ↗
die iso 27001 compliance checkliste ↗
Modified Source ↗
die soc 2 compliance checkliste ↗
Modified Source ↗
what is grc ↗
Modified Source ↗
building trust in the ai era unifying security risk and privacy ↗
Modified Source ↗
building trust in the ai era unifying security risk and privacy ↗
Modified Source ↗
defensive networks ↗
Modified Source ↗
soci ↗
Modified Source ↗
risk mitigation strategies ↗
Modified Source ↗
speakers ↗
Modified Source ↗
grc metrics measurement ↗
Modified Source ↗
valkyries game sept 18 ↗
Modified Source ↗
run compliance from claude cursor and codex with vanta ↗
Modified Source ↗
run compliance from claude cursor and codex build with vanta ↗
Modified Source ↗
pa consulting ↗
Modified Source ↗
bonafi ↗
Modified Source ↗
c5 2026 readiness checklist ↗
Modified Source ↗
the c5 2026 readiness checklist ↗
Modified Source ↗
compliance audit ↗
Modified Source ↗
grc automation ↗
Modified Source ↗
security reviews ↗
Modified Source ↗
snowfire ↗
Modified Source ↗
forvis mazars ↗
Modified Source ↗
soc 2 compliance checklist ↗
Modified Source ↗
us open september 1 ↗
Modified Source ↗
iru ↗
Modified Source ↗
smartsheet ↗
Modified Source ↗
slack ↗
Modified Source ↗
twilio ↗
Modified Source ↗
vanta trust center on aws marketplace ↗
Modified Source ↗
cybersecurity regulations frameworks healthcare ↗
Modified Source ↗
global ↗
Modified Source ↗
what is grc engineering a fresh take on an old space apj ↗
Modified Source ↗
compliance meets ai designing products that are secure from the start with vanta and aws ↗
Modified Source ↗
compliance meets ai designing products that are secure from the start with vanta and aws ↗
Modified Source ↗
press ↗
Modified Source ↗
new in vanta september 2022 ↗
Modified Source ↗
pci compliance for small businesses what you need to know ↗
Modified Source ↗
pci compliance in 3 steps ↗
Modified Source ↗
point in time vs continuous monitoring for security ↗
Modified Source ↗
risk assessment 101 working backwards from the controls ↗
Modified Source ↗
security vs compliance whats the difference ↗
Modified Source ↗
the importance of hipaa and what it can mean for your business ↗
Modified Source ↗
the roles of pci dss and hipaa compliance ↗
Modified Source ↗
the ultimate guide to nist 800 53 ↗
Modified Source ↗
third party risk management data insights ↗
Modified Source ↗
understanding the value of soc 2 compliance for your company ↗
Modified Source ↗
vanta and fintech infrastructure introduce the open finance data security standard ofdss ↗
Modified Source ↗
vanta crosses 500 raving reviews on g2 ↗
Modified Source ↗
vanta is iso 27001 certified ↗
Modified Source ↗
vanta recap security for b2b sales webinar with yc ↗
Modified Source ↗
what are the benefits of a pci automated platform ↗
Modified Source ↗
what is nist csf and why is it important ↗
Modified Source ↗
what is pci compliance a pci dss overview ↗
Modified Source ↗
what is the ccpa and how will it affect your company ↗
Modified Source ↗
what is vendor compliance ↗
Modified Source ↗
whats new in vanta 8 31 21 ↗
Modified Source ↗
which industries are most likely to ask for a soc 2 report ↗
Modified Source ↗
why companies that use stripe still need pci compliance ↗
Modified Source ↗
why should my company comply with a higher level of pci compliance ↗
Modified Source ↗
your ccpa guide to data privacy compliance ↗
Modified Source ↗
your guide to ecommerce pci compliance ↗
Modified Source ↗
what is grc engineering a fresh take on an old space ↗
Modified Source ↗
what is grc engineering a fresh take on an old space ↗
Modified Source ↗
what is grc engineering a fresh take on an old space ↗
Modified Source ↗
cybersecurity maturity assessment template ↗
Modified Source ↗
minimize third party risk with strong vendor management ↗
Modified Source ↗
the ciso playbook how security leaders at calm perforce xactus and vanta drive outcomes ↗
Modified Source ↗
periculo ↗
Modified Source ↗
how gdpr iso and soc 2 can level up your selling game ↗
Modified Source ↗
how to secure your cardholder data environment and gain pci dss compliance ↗
Modified Source ↗
how to set up your security to scale overseas ↗
Modified Source ↗
iso 27001 2022 updates and what they mean for your organization ↗
Modified Source ↗
iso 27001 2022 whats changed and what it means for your business ↗
Modified Source ↗
new in vanta june 2023 ↗
Modified Source ↗
tempoaudits ↗
Modified Source ↗
how long is cyber essentials valid for ↗
Modified Source ↗
centralized risk compliance ↗
Modified Source ↗
compliance risk management ↗
Modified Source ↗
grc engineering values ↗
Modified Source ↗
hipaa and hitech ↗
Modified Source ↗
hipaa and soc 2 ↗
Modified Source ↗
hipaa compliance checklist guide ↗
Modified Source ↗
iso 27001 annex a controls ↗
Modified Source ↗
iso 27001 for startups ↗
Modified Source ↗
who needs iso 27001 certification ↗
Modified Source ↗
iso 27001 vs soc 2 mapping ↗
Modified Source ↗
soc 1 vs soc 2 vs soc 3 ↗
Modified Source ↗
soc 2 policy templates ↗
Modified Source ↗
soc 2 readiness assessment checklist ↗
Modified Source ↗
soc 2 vs soc 3 whats the difference ↗
Modified Source ↗
ai insurance ↗
Modified Source ↗
8 facts about gdpr compliance you need to know ↗
Modified Source ↗
access review software guide ↗
Modified Source ↗
agentic ai security challenges ↗
Modified Source ↗
aws pci compliance what you should know ↗
Modified Source ↗
cybersecurity vs information security whats the difference ↗
Modified Source ↗
delaying compliance ↗
Modified Source ↗
differentiator among compliance automation software risk assessment register ↗
Modified Source ↗
do companies that use shopify need to be pci compliant ↗
Modified Source ↗
do you need penetration testing for compliance ↗
Modified Source ↗
for ctos 5 strategies to get buy in from your organization for information security ↗
Modified Source ↗
guide to pci compliance cost ↗
Modified Source ↗
how we build ai products at vanta ↗
Modified Source ↗
vanta ai quality evaluation maturity model ↗
Modified Source ↗
vantas agent development principles ↗
Modified Source ↗
where thinking in engineering happens now ↗
Modified Source ↗
valkyries game ↗
Modified Source ↗
auditors ↗
Modified Source ↗
roller ↗
Modified Source ↗
echelon risk cyber ↗
Modified Source ↗
eastandart inc ↗
Modified Source ↗
how to request security budget from your cfo and exec teams ↗
Modified Source ↗
what is compliance software ↗
Modified Source ↗
iso 27001 audit ↗
Modified Source ↗
resources ↗
Modified Source ↗
agentic compliance in action with vanta and claude ↗
Modified Source ↗
agentic compliance in action with vanta and claude ↗
Modified Source ↗
agentic compliance in action with vanta and claude ↗
Modified Source ↗
sigq ↗
Modified Source ↗
tikpay ↗
Modified Source ↗
rakkar digital ↗
Modified Source ↗
simetrik ↗
Modified Source ↗
splunk enterprise ↗
Modified Source ↗
grc ↗
Modified Source ↗
risk treatment options ↗
Modified Source ↗
weel ↗
Modified Source ↗
new in vanta june 2026 ↗
Modified Source ↗
common controls framework ↗
Modified Source ↗
iso 42001 certification checklist guide ↗
Modified Source ↗
quantitative and qualitative risk analysis ↗
Modified Source ↗
the iso 27001 compliance checklist ↗
Modified Source ↗
iso 27001 controls ↗
Modified Source ↗
nist ai rmf and iso 42001 ↗
Modified Source ↗
jetbrains ↗
Modified Source ↗
iso 42001 and eu ai act ↗
Modified Source ↗
nist ai rmf and iso 42001 ↗
Modified Source ↗
introducing automated iso 27001 and hipaa compliance ↗
Modified Source ↗
introducing iso 42001 ↗
Modified Source ↗
iso 27001 compliance checklist ↗
Modified Source ↗
the iso 27001 compliance checklist ↗
Modified Source ↗
vanta earns iso 42001 certification ↗
Modified Source ↗
vciso managed security services ↗
Modified Source ↗
cyber essentials and iso 27001 ↗
Modified Source ↗
hitrust and iso 27001 ↗
Modified Source ↗
beyond the first audit ↗
Modified Source ↗
risk management policy template ↗
Modified Source ↗
4 lessons learned during our iso 42001 audit ↗
Modified Source ↗
build risk taxonomy ↗
Modified Source ↗
inherent risk and residual risk ↗
Modified Source ↗
iso 27001 and cps 234 ↗
Modified Source ↗
iso 27001 compliance for healthcare ↗
Modified Source ↗
iso 42001 and eu ai act ↗
Modified Source ↗
nis 2 and iso 27001 ↗
Modified Source ↗
risk management policy ↗
Modified Source ↗
the new supply chain blast radius ↗
Modified Source ↗
new in vanta may 2026 ↗
Modified Source ↗
vanta delivers direct from new york apj ↗
Modified Source ↗
sprinto alternatives ↗
Modified Source ↗
best vendor risk management software ↗
Modified Source ↗
risk appetite statement ↗
Modified Source ↗
axipro ↗
Modified Source ↗
template ai security assessment ↗
Modified Source ↗
startup global expansion checklist ↗
Modified Source ↗
risk appetite and risk tolerance ↗
Modified Source ↗
startup global expansion checklist ↗
Modified Source ↗
the startup global expansion checklist ↗
Modified Source ↗
wizer ↗
Modified Source ↗
atruent ↗
Modified Source ↗
iso 27001 certification cost ↗
Modified Source ↗
vanta delivers live from new york ↗
Modified Source ↗
vanta delivers live from new york ↗
Modified Source ↗
vanta delivers live from new york ↗
Modified Source ↗
perk ↗
Modified Source ↗
introducing the vanta community ↗
Modified Source ↗
kobaltio ↗
Modified Source ↗
vanta delivers tprm ↗
Modified Source ↗
vanta delivers agent for risk ↗
Modified Source ↗
5 must haves in automated security ↗
Modified Source ↗
disaster recovery plan template ↗
Modified Source ↗
gdpr compliance checklist ↗
Modified Source ↗
hipaa compliance checklist ↗
Modified Source ↗
incident response plan template ↗
Modified Source ↗
iso 27001 internal audit checklist ↗
Modified Source ↗
the audit ready checklist ↗
Modified Source ↗
the iso 42001 compliance checklist ↗
Modified Source ↗
the soc 2 compliance checklist ↗
Modified Source ↗
your free iso 27001 documentation policy template ↗
Modified Source ↗
hiring 10x engineers at anthropic ↗
Modified Source ↗
how synthesia became one of europes fastest growing ai companies frameworks for growth ↗
Modified Source ↗
how to sell enterprise companies as an ai startup ↗
Modified Source ↗
replit future of code ↗
Modified Source ↗
vanta acquires riskey ↗
Modified Source ↗
vanta crosses 300m in arr as growth accelerates ↗
Modified Source ↗
vanta delivers adaptive scoping ↗
Modified Source ↗
vanta delivers calmpliance ↗
Modified Source ↗
vanta delivers compliance agent ↗
Modified Source ↗
vanta delivers customer trust agent ↗
Modified Source ↗
vanta delivers information request lists ↗
Modified Source ↗
vanta delivers privacy automation ↗
Modified Source ↗
vanta delivers tprm agent ↗
Modified Source ↗
vanta delivers vanta control framework ↗
Modified Source ↗
why the next unicorns are built by ai ↗
Modified Source ↗
videos ↗
Modified Source ↗
hyperproof alternatives ↗
Modified Source ↗
new york ↗
Modified Source ↗
forrester wave download ↗
Modified Source ↗
compliance risk ↗
Modified Source ↗
cyber risk institute profile ↗
Modified Source ↗
how to develop an effective disaster recovery plan ↗
Modified Source ↗
security communication report ↗
Modified Source ↗
vanta vs drata vs auditboard ↗
Modified Source ↗
nominations 25 to trust ↗
Modified Source ↗
vanta a forrester grc wave leader ↗
Modified Source ↗
continuous control monitoring ↗
Modified Source ↗
vantacon uk 2026 recap ↗
Modified Source ↗
auditor basics a 30 minute guide for startups ↗
Modified Source ↗
auditor basics a 30 minute guide for startups ↗
Modified Source ↗
auditor basics a 30 minute guide for startups ↗
Modified Source ↗
why cheaper code isnt always cheap ↗
Modified Source ↗
ghosteye ↗
Modified Source ↗
ghosteye ↗
Modified Source ↗
edamametechnologies ↗
Modified Source ↗
ai compliance ↗
Modified Source ↗
it compliance audit checklist 7 steps to follow ↗
Modified Source ↗
questions for security questionnaires ↗
Modified Source ↗
who needs to comply with dora ↗
Modified Source ↗
dora compliance checklist ↗
Modified Source ↗
ai broke your third party risk management program now what apj ↗
Modified Source ↗
the us data privacy checklist ↗
Modified Source ↗
the us data privacy checklist ↗
Modified Source ↗
us data privacy checklist ↗
Modified Source ↗
vibrent health ↗
Modified Source ↗
uk ↗
Modified Source ↗
wetransform ↗
Modified Source ↗
the soc 2 compliance checklist ↗
Modified Source ↗
deal registration ↗
Modified Source ↗
ransonleak ↗
Modified Source ↗
ransomleak ↗
Modified Source ↗
ai broke your third party risk management program now what ↗
Modified Source ↗
ai broke your third party risk management program now what ↗
Modified Source ↗
ai broke your third party risk management program now what ↗
Modified Source ↗
samsara ↗
Modified Source ↗
on demand demo replay ↗
Modified Source ↗
onetrust alternatives ↗
Modified Source ↗
iso 27001 risk assessment ↗
Modified Source ↗
iso 27001 vs iso 27002 ↗
Modified Source ↗
learn how to automate compliance for soc 2 iso 27001 and more q2 ↗
Modified Source ↗
learn how to automate compliance for soc 2 iso 27001 and more q2 ↗
Modified Source ↗
turn every promise into predictable trust customer commitments in action apj ↗
Modified Source ↗
berlin ↗
Modified Source ↗
cmmc checklist ↗
Modified Source ↗
compliance for startups bundle ↗
Modified Source ↗
on demand demo ↗
Modified Source ↗
secureframe alternatives ↗
Modified Source ↗
bia template ↗
Modified Source ↗
bia template ↗
Modified Source ↗
europe regulations and vendor risk ↗
Modified Source ↗
elevate trust tour ny ↗
Modified Source ↗
optro alternatives ↗
Modified Source ↗
grc engineering vs traditional grc ↗
Modified Source ↗
grc engineering implementation guide ↗
Modified Source ↗
benefits of grc engineering ↗
Modified Source ↗
what is grc engineering ↗
Modified Source ↗
grc engineering ↗
Modified Source ↗
australian startup global expansion checklist ↗
Modified Source ↗
australian startup global expansion checklist ↗
Modified Source ↗
drata alternatives ↗
Modified Source ↗
the australian startups global expansion checklist ↗
Modified Source ↗
statement of applicability iso 27001 ↗
Modified Source ↗
hyperbound ↗
Modified Source ↗
ai agents lacking ai policies ↗
Modified Source ↗
from pilot to moderate lessons from vantas fedramp 20x journey ↗
Modified Source ↗
demo ↗
Modified Source ↗
tprm ↗
Modified Source ↗
clearbit cri test ↗
Modified Source ↗
new in vanta april 2026 ↗
Modified Source ↗
vanta donates aarm to csa ↗
Modified Source ↗
germany ↗
Modified Source ↗
france ↗
Modified Source ↗
australia ↗
Modified Source ↗
demo apac ↗
Modified Source ↗
idc business value roi white paper ↗
Modified Source ↗
upgrade to vanta ↗
Modified Source ↗
trust ↗
Modified Source ↗
hipaa ↗
Modified Source ↗
iso 27001 ↗
Modified Source ↗
soc 2 ↗
Modified Source ↗
automation value calculator ↗
Modified Source ↗
msp onboarding activation ↗
Modified Source ↗
demo fr ↗
Modified Source ↗
demo ai ↗
Modified Source ↗
aws marketplace ↗
Modified Source ↗
research ↗
Modified Source ↗
security ↗
Modified Source ↗
msp draft 2 ↗
Modified Source ↗
continuous trust ↗
Modified Source ↗
privacy foundations ↗
Modified Source ↗
security and compliance foundations ↗
Modified Source ↗
multinational operations ↗
Modified Source ↗
the ai governance checklist ↗
Modified Source ↗
turn every promise into predictable trust customer commitments in action ↗
Modified Source ↗
turn every promise into predictable trust customer commitments in action ↗
Modified Source ↗
turn every promise into predictable trust customer commitments in action ↗
Modified Source ↗
ai sprawl governance ↗
Modified Source ↗
ai agent audit preparation ↗
Modified Source ↗
cmmc checklist ↗
Modified Source ↗
how we built authorization as a platform lessons from scaling fine grained access controls at vanta ↗
Modified Source ↗
the cmmc checklist ↗
Modified Source ↗
soc 2 basics a 30 minute guide for startups ↗
Modified Source ↗
soc 2 basics a 30 minute guide for startups ↗
Modified Source ↗
soc 2 basics a 30 minute guide for startups ↗
Modified Source ↗
automate compliance and stay audit ready with vanta ↗
Modified Source ↗
automate compliance and stay audit ready with vanta ↗
Modified Source ↗
business continuity plan template ↗
Modified Source ↗
intruder ↗
Modified Source ↗
carahsoft ↗
Modified Source ↗
additional resources ↗
Modified Source ↗
how to choose iso 42001 compliance software ↗
Modified Source ↗
introduction ↗
Modified Source ↗
iso 42001 audit ↗
Modified Source ↗
iso 42001 auditors ↗
Modified Source ↗
iso 42001 certification cost ↗
Modified Source ↗
iso 42001 certification process and timeline ↗
Modified Source ↗
iso 42001 controls ↗
Modified Source ↗
iso 42001 requirements ↗
Modified Source ↗
maintaining iso 42001 compliance ↗
Modified Source ↗
preparing for certification ↗
Modified Source ↗
requirements ↗
Modified Source ↗
roles in iso 42001 ↗
Modified Source ↗
who needs iso 42001 ↗
Modified Source ↗
ygisolutions ↗
Modified Source ↗
how security leaders can safely and effectively implement agentic ai ↗
Modified Source ↗
learn how to automate compliance for soc 2 iso 27001 and more with vanta ↗
Modified Source ↗
atoro ↗
Modified Source ↗
cyberally ↗
Modified Source ↗
grcconcierge ↗
Modified Source ↗
rhymetec ↗
Modified Source ↗
securepoint360llc ↗
Modified Source ↗
tagoreas ↗
Modified Source ↗
workstreet ↗
Modified Source ↗
hipaa ↗
Modified Source ↗
soc 2 ↗
Modified Source ↗
iso 27001 ↗
Modified Source ↗
home ↗
Modified Source ↗
grc ↗
Modified Source ↗
compliance automation ↗
Modified Source ↗
hipaa ↗
Modified Source ↗
gdpr ↗
Modified Source ↗
iso 27001 ↗
Modified Source ↗
home ↗
Modified Source ↗
demo ↗
Modified Source ↗
grc ↗
Modified Source ↗
compliance automation ↗
Modified Source ↗
gdpr ↗
Modified Source ↗
demo trust ↗
Modified Source ↗
trelica ↗
Modified Source ↗
succeedlearn ↗
Modified Source ↗
hirepass ↗
Modified Source ↗
griffo ↗
Modified Source ↗
capturethebug ↗
Modified Source ↗
bocada ↗
Modified Source ↗
almanax ↗
Modified Source ↗
latticeflowai ↗
Modified Source ↗
outkept ↗
Modified Source ↗
vanta is a leader in the idc marketscape ↗
Modified Source ↗
demo eu ↗
Modified Source ↗
demo risk ↗
Modified Source ↗
event ↗
Modified Source ↗
integration partners ↗
Modified Source ↗
goodbye audit chaos hello calm pliance ↗
Modified Source ↗
goodbye audit chaos hello calm pliance apj ↗
Modified Source ↗
how do you perform quarterly access reviews ↗
Modified Source ↗
noibu ↗
Modified Source ↗
pinpoint ↗
Modified Source ↗
building a comprehensive trust center ↗
Modified Source ↗
hitrust ↗
Modified Source ↗
home ↗
Modified Source ↗
iso 27001 ↗
Modified Source ↗
iso 27001 compliance ↗
Modified Source ↗
iso 42001 ↗
Modified Source ↗
nis2 ↗
Modified Source ↗
pci ↗
Modified Source ↗
soc 2 compliance for startups ↗
Modified Source ↗
soc 2 compliance software ↗
Modified Source ↗
soc 2 report ↗
Modified Source ↗
soc 2 soc type 2 ↗
Modified Source ↗
vendor risk management ↗
Modified Source ↗
vrm ↗
Modified Source ↗
cmmc ↗
Modified Source ↗
compliance automation ↗
Modified Source ↗
communicate the value of preventative security ↗
Modified Source ↗
communicate the value of preventative security ↗
Modified Source ↗
beyond the checkbox scaling compliance across european regulations ↗
Modified Source ↗
beyond the checkbox scaling compliance across european regulations ↗
Modified Source ↗
beyond the checkbox scaling compliance across european regulations ↗
Modified Source ↗
customer commitments in action ↗
Modified Source ↗
barradvisory ↗
Modified Source ↗
aprio ↗
Modified Source ↗
prescientsecurity ↗
Modified Source ↗
johansongroup ↗
Modified Source ↗
insightassurance ↗
Modified Source ↗
learn how to automate soc 2 iso 27001 more ↗
Modified Source ↗
learn how to automate soc 2 iso 27001 and more ↗
Modified Source ↗
new in vanta march 2026 ↗
Modified Source ↗
the soc 2 compliance checklist 2 ↗
Modified Source ↗
incident response plan template ↗
Modified Source ↗
rad ai ↗
Modified Source ↗
vanta vs drata vs delve ↗
Modified Source ↗
regulatory compliance software guide ↗
Modified Source ↗
5 key questions to ask your auditor ↗
Modified Source ↗
celebrating new milestones ↗
Modified Source ↗
automating soc 2 compliance more 2 ↗
Modified Source ↗
automate soc 2 customer stories ↗
Modified Source ↗
compliance benchmark report 24 ↗
Modified Source ↗
simplifying soc 2 and iso 27001 compliance for growing businesses ↗
Modified Source ↗
live demo how to streamline iso 27001 and soc 2 compliance with automation ↗
Modified Source ↗
breachrx ↗
Modified Source ↗
charityvest ↗
Modified Source ↗
hummingbird healthcare ↗
Modified Source ↗
audit outdated security processes ↗
Modified Source ↗
railway ↗
Modified Source ↗
tailscale ↗
Modified Source ↗
subrosa ↗
Modified Source ↗
splunk ↗
Modified Source ↗
primo ↗
Modified Source ↗
simplebackups ↗
Modified Source ↗
plerion ↗
Modified Source ↗
osano ↗
Modified Source ↗
ostorlab ↗
Modified Source ↗
moxso ↗
Modified Source ↗
fourfour ↗
Modified Source ↗
cyberly ↗
Modified Source ↗
keeper ↗
Modified Source ↗
edamametechnologies ↗
Modified Source ↗
fieldguide ↗
Modified Source ↗
remote 0ea78 ↗
Modified Source ↗
peripass ↗
Modified Source ↗
parsable 2be44 ↗
Modified Source ↗
priorityMatrix ↗
Modified Source ↗
hello id ↗
Modified Source ↗
hook ↗
Modified Source ↗
H5mag ↗
Modified Source ↗
slab f4781 ↗
Modified Source ↗
eletive ↗
Modified Source ↗
elium 0b4cf ↗
Modified Source ↗
clebex a9248 ↗
Modified Source ↗
exium e8290 ↗
Modified Source ↗
drift 3d485 ↗
Modified Source ↗
cleanmail f734a ↗
Modified Source ↗
blogIn ↗
Modified Source ↗
cinode 24f49 ↗
Modified Source ↗
audora ↗
Modified Source ↗
blinq ↗
Modified Source ↗
atmos ↗
Modified Source ↗
alertMedia ↗
Modified Source ↗
abv ↗
Modified Source ↗
appaegis 76b4c ↗
Modified Source ↗
manage engine ↗
Modified Source ↗
sclaeai ↗
Modified Source ↗
Probely ↗
Modified Source ↗
harvest ed10a ↗
Modified Source ↗
payfit 95f52 ↗
Modified Source ↗
asset panda ↗
Modified Source ↗
ramp 951f2 ↗
Modified Source ↗
torq ↗
Modified Source ↗
wiz 90572 ↗
Modified Source ↗
opsgenie 1f68e ↗
Modified Source ↗
automox 51139 ↗
Modified Source ↗
microsoft planner ↗
Modified Source ↗
payfit ↗
Modified Source ↗
openai b32e1 ↗
Modified Source ↗
ovh cloud ↗
Modified Source ↗
oyster f536d ↗
Modified Source ↗
appaegis faa44 ↗
Modified Source ↗
adobelearning 698ef ↗
Modified Source ↗
three sixty learning ↗
Modified Source ↗
robin 747f6 ↗
Modified Source ↗
payworks 86a75 ↗
Modified Source ↗
zinc 03a0e ↗
Modified Source ↗
defender gcc high ↗
Modified Source ↗
intune gcc high ↗
Modified Source ↗
entra gcc high ↗
Modified Source ↗
miradore ↗
Modified Source ↗
goodbye audit chaos hello calm pliance ↗
Modified Source ↗
goodbye audit chaos hello calm pliance ↗
Modified Source ↗
security capabilities for startups ↗
Modified Source ↗
ai governance checklist ↗
Modified Source ↗
ai governance checklist ↗
Modified Source ↗
fedramp ↗
Modified Source ↗
accumulus technologies ↗
Modified Source ↗
acme technology ↗
Modified Source ↗
ashby ↗
Modified Source ↗
atlassian ↗
Modified Source ↗
audiostack ↗
Modified Source ↗
belvo ↗
Modified Source ↗
black kite ↗
Modified Source ↗
bvnk ↗
Modified Source ↗
bynder ↗
Modified Source ↗
cable ↗
Modified Source ↗
cedar ↗
Modified Source ↗
chili piper ↗
Modified Source ↗
cipherstash ↗
Modified Source ↗
clay ↗
Modified Source ↗
clozd ↗
Modified Source ↗
coachhub ↗
Modified Source ↗
complycube ↗
Modified Source ↗
coviu ↗
Modified Source ↗
coxwave ↗
Modified Source ↗
crypdefi ↗
Modified Source ↗
dagger ↗
Modified Source ↗
docgo ↗
Modified Source ↗
dovetail ↗
Modified Source ↗
duolingo ↗
Modified Source ↗
everlab ↗
Modified Source ↗
factory ↗
Modified Source ↗
fern ↗
Modified Source ↗
fileai ↗
Modified Source ↗
fireant ↗
Modified Source ↗
flo health ↗
Modified Source ↗
fujitsu launchpad ↗
Modified Source ↗
github ↗
Modified Source ↗
granola ↗
Modified Source ↗
healthie ↗
Modified Source ↗
incentx ↗
Modified Source ↗
incident io ↗
Modified Source ↗
ironclad ↗
Modified Source ↗
josef ↗
Modified Source ↗
keeper ↗
Modified Source ↗
leantaas ↗
Modified Source ↗
leapsome ↗
Modified Source ↗
leela ai ↗
Modified Source ↗
lemba therapeutics ↗
Modified Source ↗
maltego ↗
Modified Source ↗
master electronics ↗
Modified Source ↗
modern health ↗
Modified Source ↗
moonpay ↗
Modified Source ↗
neuralift ai ↗
Modified Source ↗
newfront ↗
Modified Source ↗
nominal ↗
Modified Source ↗
peak ↗
Modified Source ↗
perforce ↗
Modified Source ↗
pigment ↗
Modified Source ↗
pigment french ↗
Modified Source ↗
ramp ↗
Modified Source ↗
reachdesk ↗
Modified Source ↗
recidiviz ↗
Modified Source ↗
registrar corp ↗
Modified Source ↗
shipbob ↗
Modified Source ↗
shortcut ↗
Modified Source ↗
sitoo ↗
Modified Source ↗
slope software ↗
Modified Source ↗
snowflake ↗
Modified Source ↗
solidroad ↗
Modified Source ↗
squadify ↗
Modified Source ↗
stormboard ↗
Modified Source ↗
supabase ↗
Modified Source ↗
tactiq ↗
Modified Source ↗
tailor ↗
Modified Source ↗
taptap send ↗
Modified Source ↗
the mj companies ↗
Modified Source ↗
traffyk ai ↗
Modified Source ↗
typeform ↗
Modified Source ↗
unleash ↗
Modified Source ↗
upflow french ↗
Modified Source ↗
us med equip ↗
Modified Source ↗
userevidence ↗
Modified Source ↗
veriff ↗
Modified Source ↗
versa ↗
Modified Source ↗
workjam ↗
Modified Source ↗
writer ↗
Modified Source ↗
yellow canary ↗
Brand colors & fonts
Observed website styles · partial · Nov 11, 2026
accent · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗primary · inferred
Source ↗accent · inferred
Source ↗accent · inferred
Source ↗accent · inferred
Source ↗accent · inferred
Source ↗accent · inferred
Source ↗accent · inferred
Source ↗sans-serif
body · declared in stylesheet ·
Fallback: system-ui, sans-serif
Arial
body · declared in stylesheet ·
Fallback: system-ui, sans-serif
Soehne
body · declared in stylesheet · 400, 300, 600, 500
Fallback: system-ui, sans-serif
SC Ripley
heading · declared in stylesheet · 300, 400, 500, 100, 200
Fallback: system-ui, sans-serif
Soehne
other · declared in stylesheet · 400, 300, 600, 500
Fallback: system-ui, sans-serif
Nib Pro
other · declared in stylesheet · 600
Fallback: system-ui, sans-serif
Reckless
other · declared in stylesheet · 700, 300, 500, 400
Fallback: system-ui, sans-serif
SC Ripley
other · declared in stylesheet · 300, 400, 500, 100, 200
Fallback: system-ui, sans-serif
Disclaimer: These samples are not verified official brand guidelines or a complete palette. Previews use system fonts; font licensing, reuse and redistribution rights are unverified. Font URLs are evidence only. Actual rendering and loaded fonts may differ; displayed font names may be simplified.
Collection details
CSS declarations only; browser rendering, cascade, active theme, loaded fonts and official brand guidelines have not been verified. Generated font aliases are normalized for display; exact declarations remain in cssFamily. Colors are semantic declaration samples converted to sRGB, not an exhaustive palette. Font asset URLs are evidence only; license and redistribution rights are unknown.
Contact
Contact forms
- Get a demo ↗
- Request a demo ↗/demo-ai
- Request a demo ↗/products/ai
- Book a demo ↗/products/ai-governance
- Book a demo ↗/products/ai-governance
- Request a demo ↗/products/audit
- Request a demo ↗/products/automated-compliance
- Request a demo ↗/products/custom-frameworks
- Request a demo ↗/products/customer-commitments
- Request a demo ↗/products/fedramp
- Request a demo ↗/products/gdpr
- Request a demo ↗/products/grc
- Request a demo ↗/products/hipaa
- Request a demo ↗/products/hitrust
- Request a demo ↗/products/iso-27001
- Request a demo ↗/products/iso-42001
- Request a demo ↗/products/nist-ai-risk-management-framework
- Request a demo ↗/products/personnel-access
- Request a demo ↗/products/questionnaire-automation
- Request a demo ↗/products/risk
- Request a demo ↗/products/soc-2
- Request a demo ↗/products/third-party-risk-management